Windows WalletService Vulnerability: Local Privilege Escalation Poses System-Level Threat A recently addressed vulnerability in Microsoft Windows’ WalletService, tracked as CVE-2026-49176, has brought to light a [...]
The open-source supply chain has become a significant attack vector, with malicious packages posing a constant threat to development pipelines and ultimately, end-user systems. For [...]
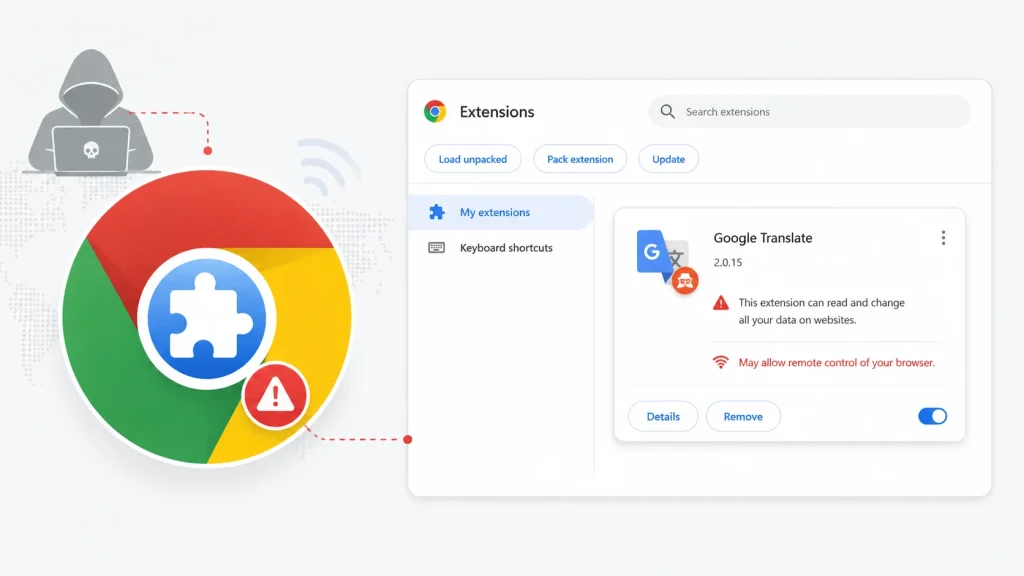
The Deceptive Disguise: Fake GoogleTranslate Extension Hijacks Browsers The digital landscape is rife with threats, and one of the most insidious forms of attack leverages [...]
A significant security flaw has emerged within Red Hat’s Advanced Cluster Management for Kubernetes (ACM), posing a critical risk to organizations leveraging this powerful platform. [...]
Stealthy Threats: Unpacking Anatsa Banking Malware’s Google Play Infiltration The digital landscape consistently reminds us that even seemingly innocuous sources can harbor significant threats. [...]
CISA Sounds Alarm: Progress LoadMaster Command Injection Vulnerability Actively Exploited The cybersecurity landscape just became a little more perilous for organizations relying on Progress LoadMaster [...]
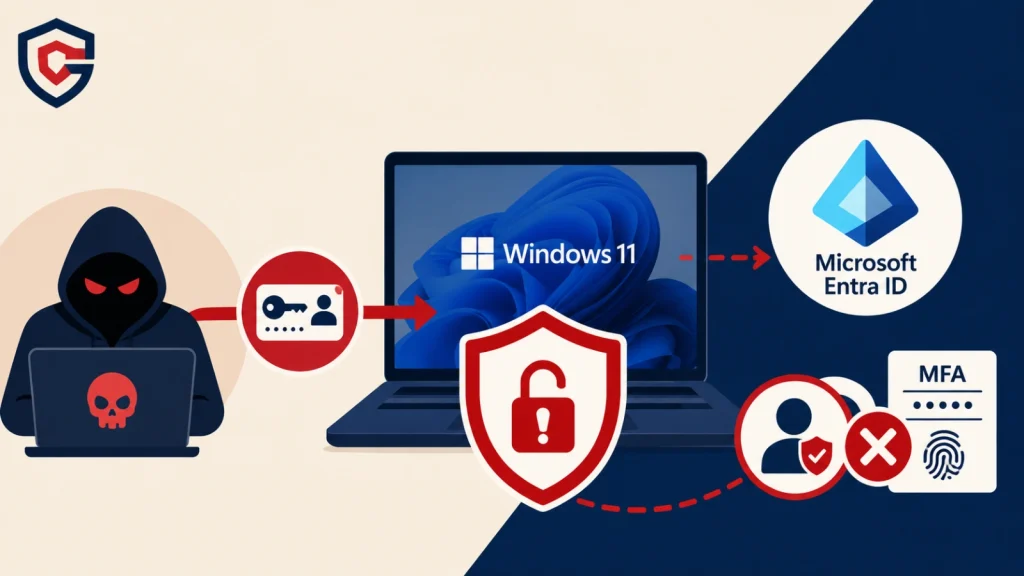
Unmasking the Threat: Pass-the-Passkey Attacks Bypass MFA on Windows 11 and Microsoft Entra ID Multi-Factor Authentication (MFA) has long been the cornerstone of strong identity [...]
In the evolving landscape of enterprise security, the integrity of endpoint devices is paramount. When foundational security mechanisms are compromised, the ripple effects can be [...]
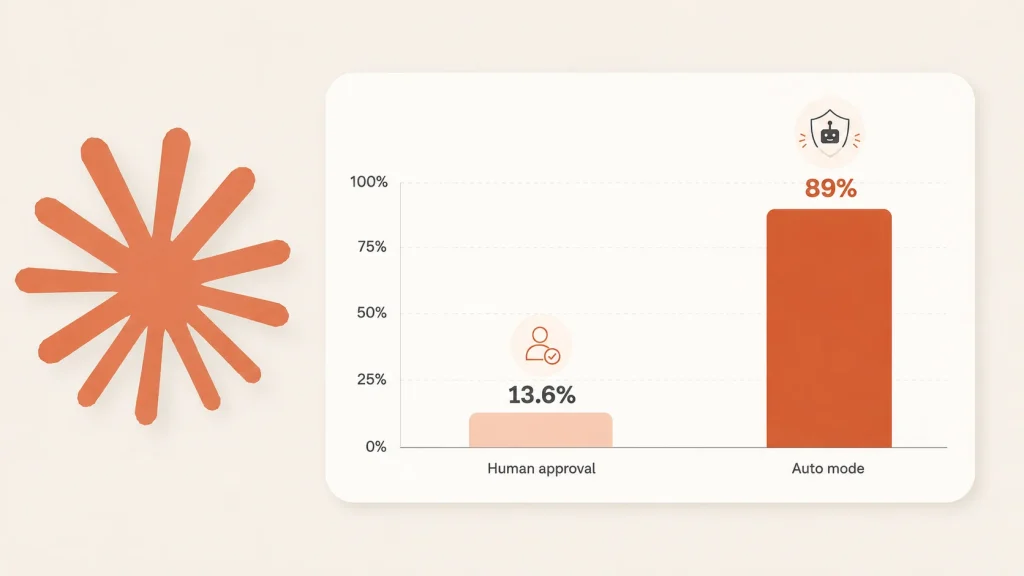
Claude Code’s Paradigm Shift: From Human Approval to Automated Agent Security The landscape of AI-assisted coding is undergoing a significant transformation, particularly in how security [...]
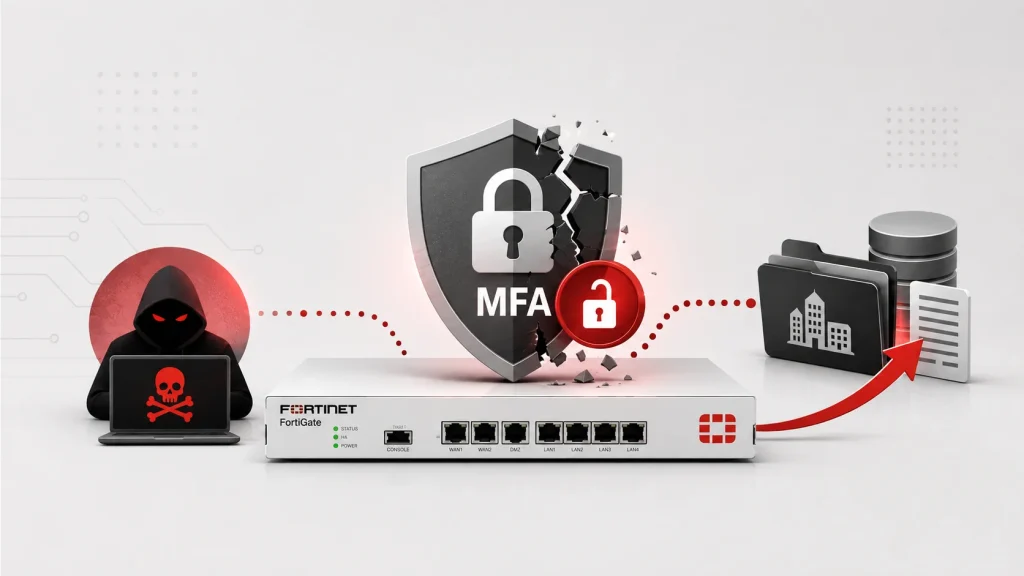
A disturbing trend in the ransomware landscape has emerged, with the Gunra ransomware group actively exploiting critical vulnerabilities within Fortinet VPN solutions. This sophisticated attack [...]
