Unmasking the Claude Tag Vulnerability: A Wake-Up Call for Enterprise Security In the dynamic landscape of enterprise communication, Slack has become an indispensable tool. Its [...]
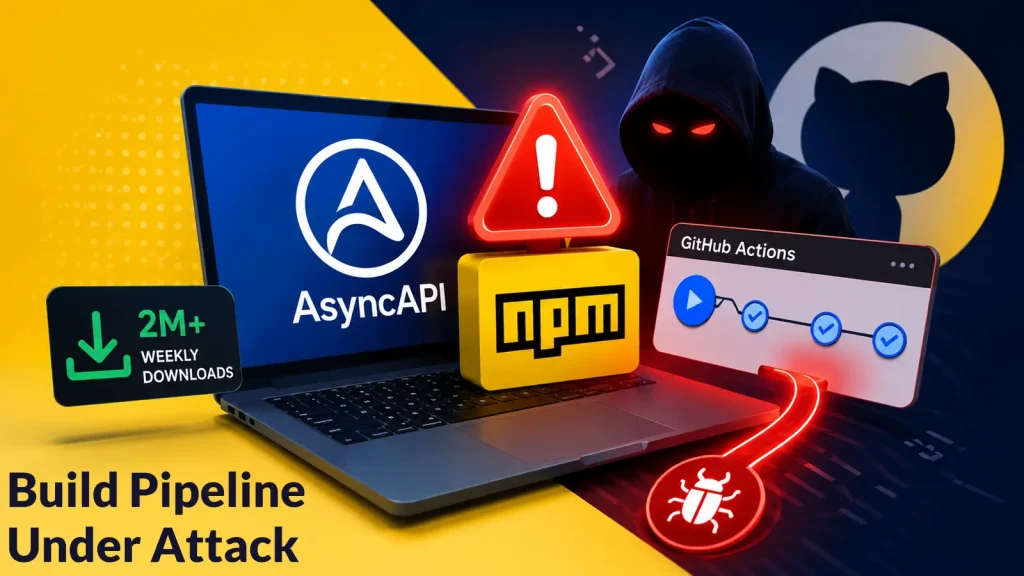
Supply Chain Nightmare: AsyncAPI npm Packages Compromised via GitHub Actions In a stark reminder of the persistent threats lurking within the software supply chain, a [...]
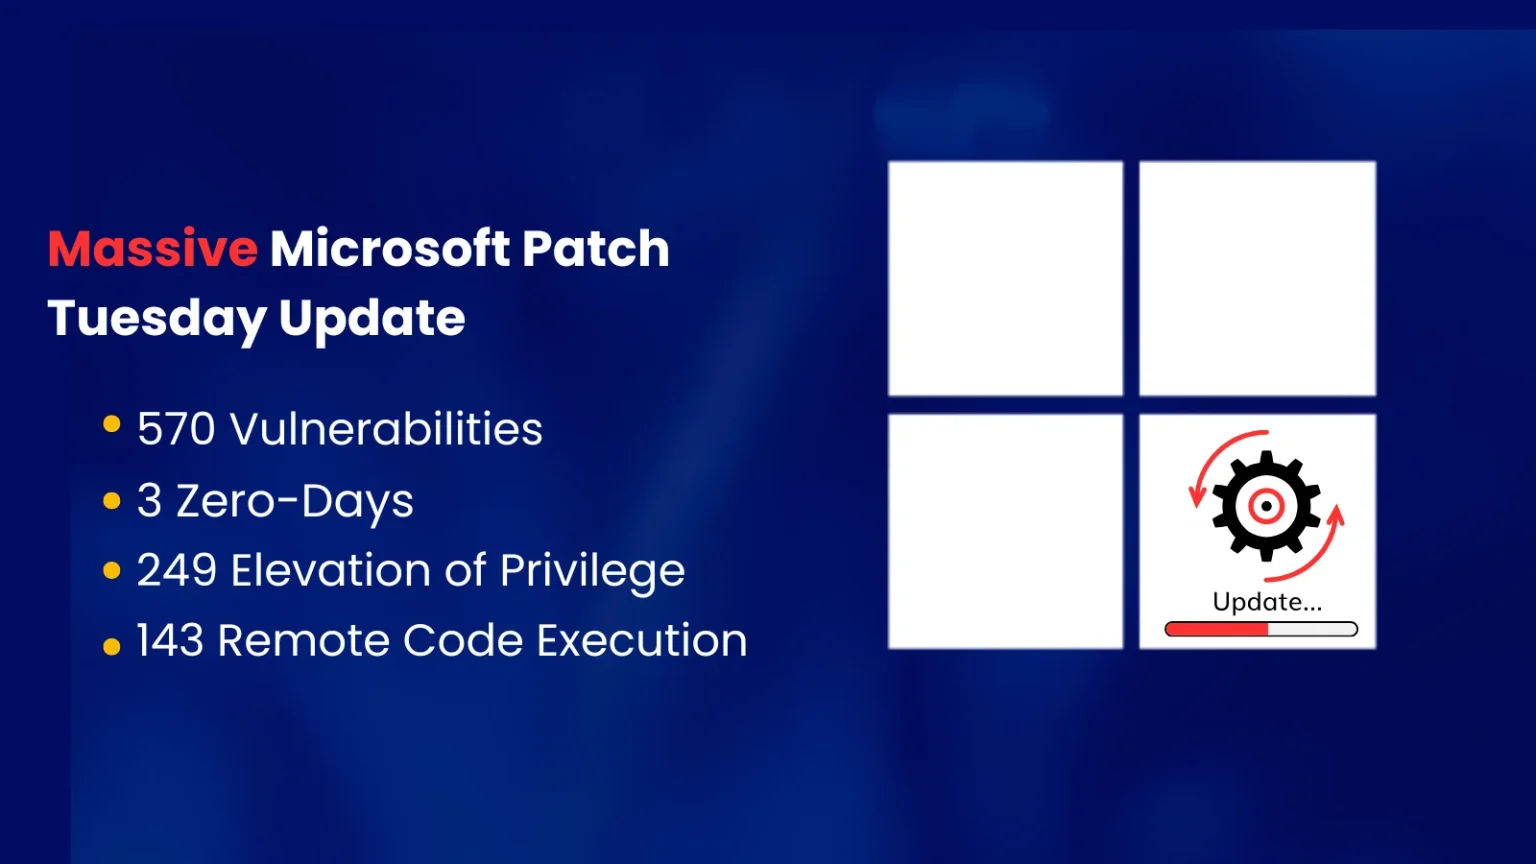
Microsoft Patch Tuesday July 2026: A Deep Dive into 570 Vulnerability Fixes Microsoft’s July 2026 Patch Tuesday has landed, delivering a monumental update that [...]
The Stealthy Threat: How Spoofed OAuth Client IDs Enumerate Entra ID Users The landscape of enterprise security faces a persistent and evolving adversary. A recent [...]
FortiSandbox Vulnerability Exposes VNC Servers: A Critical Security Alert In the dynamic landscape of cybersecurity, a recent disclosure from Fortinet highlights a high-severity vulnerability within [...]
The Silent Menace: Miasma’s Return Through Trusted npm Packages Imagine integrating a seemingly benign, widely-used software package into your development workflow, only to discover it’s [...]
A disturbing vulnerability in the Claude for Chrome browser extension has been uncovered, posing a significant risk to user privacy. This flaw allows attackers to [...]
Fortinet Patches Seven Vulnerabilities: Urgent Action for FortiOS, FortiProxy, FortiPAM, and FortiSandbox Users In a recent disclosure, Fortinet has rolled out patches for seven distinct [...]
In the relentless battle against cyber threats, security operations centers (SOCs) constantly seek advanced capabilities to outmaneuver adversaries. The sheer volume and sophistication of modern [...]
The Intelligent Worm: A Glimpse into Adaptive Malware’s Future The cybersecurity landscape has always been a battleground of innovation, with defenders striving to outmaneuver [...]