Wireless IDS/IPS: Detecting Attacks Over Wi‑Fi
Wi-Fi WIDS: Wireless Network Intrusion Detection System
In an era where digital connectivity is fundamental to business operations, the security of wireless networks has become a paramount concern. This article delves into Wireless Intrusion Detection Systems (WIDS), exploring their critical role in safeguarding Wi-Fi networks from an ever-evolving landscape of cyber threats and vulnerabilities.
Understanding Wireless Intrusion Detection Systems

What is a Wireless Intrusion Detection System (WIDS)?
A Wireless Intrusion Detection System (WIDS) is a specialized intrusion detection system meticulously designed to monitor a wireless network for suspicious activities and potential intrusions. Unlike traditional network intrusion detection systems, a WIDS focuses specifically on 802.11 Wi-Fi network traffic, analyzing wireless traffic patterns to detect anomalies, unauthorized access, and various malicious activities. Its primary function is to identify and alert administrators to wireless intrusion attempts, safeguarding the integrity and confidentiality of the Wi-Fi network.
Importance of WIDS in Cybersecurity
The importance of WIDS in contemporary cybersecurity cannot be overstated, given the inherent vulnerabilities of wireless networks. A robust WIDS solution is crucial for proactive threat detection, identifying potential threats like rogue access points, denial-of-service (DoS) attacks, and man-in-the-middle attacks before they can compromise network performance or data security. By continuously monitoring the wireless environment, WIDS provides real-time insights into the security posture of the Wi-Fi network, ensuring that any wireless intrusion is promptly identified and addressed, thereby fortifying overall network security.
Components of WIDS
A comprehensive Wireless Intrusion Detection System (WIDS) typically comprises several key components working in concert to provide robust intrusion detection and prevention. These include dedicated wireless sensors strategically placed to monitor wireless traffic, and a central management console for configuration and alert management. A powerful analysis engine is also included, capable of signature-based detection and anomaly detection.
Some advanced WIDS solutions offer additional capabilities and integrations:
| Feature | Description |
|---|---|
| IDPS Integration | Integrates with existing Intrusion Detection and and Prevention Systems. |
| Open-source Tool Leverage | Can leverage tools like Snort for enhanced threat intelligence and sophisticated attack detection. |
Intrusion Detection and Prevention Mechanisms

How Intrusion Detection Works
Intrusion detection systems, including a Wireless Intrusion Detection System (WIDS), operate by meticulously analyzing network traffic to identify patterns indicative of malicious activities or unauthorized access. This process typically involves continuous monitoring of wireless traffic against a predefined set of rules, signatures, or established baselines of normal network behavior. When an anomaly is detected, such as unusual traffic spikes or an unrecognized access point, the system generates an alert, notifying administrators in real time. This proactive approach to threat detection is crucial for mitigating potential threats before they escalate, thereby safeguarding the integrity of the Wi-Fi network and ensuring robust network security.
Intrusion Detection vs. Intrusion Prevention
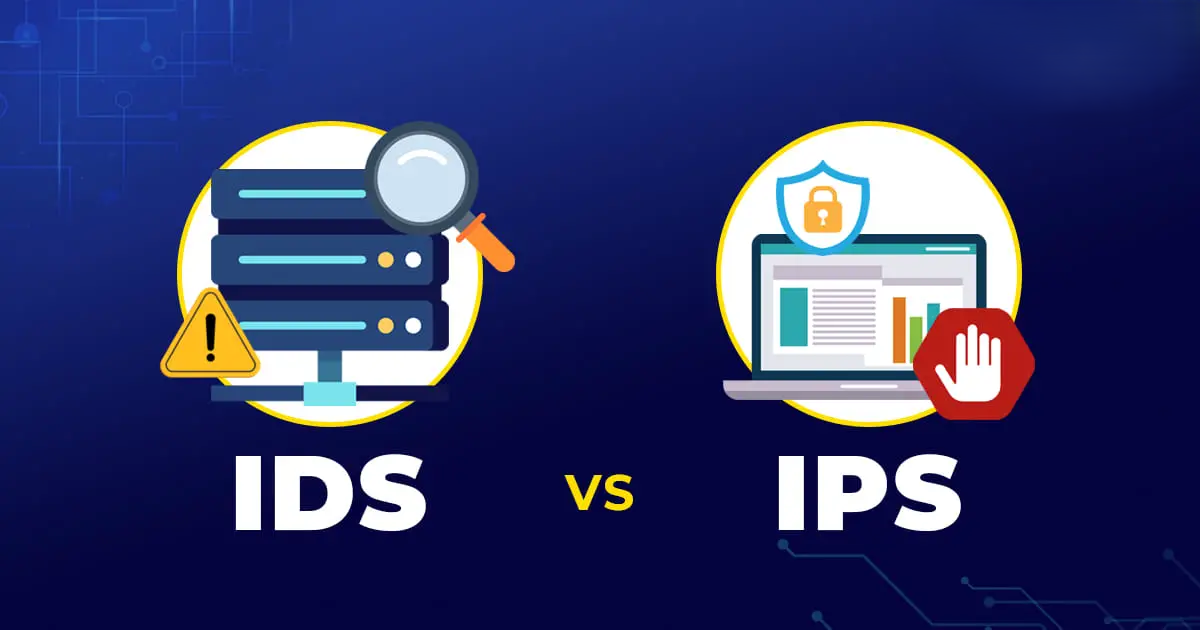
While often discussed together, intrusion detection and intrusion prevention serve distinct yet complementary functions within network security.
| System | Primary Function |
|---|---|
| Intrusion Detection System (IDS) | Identifies and alerts to potential threats and vulnerabilities; observational and reactive. |
| Intrusion Prevention System (IPS) | Actively blocks or mitigates detected threats, preventing intrusions. |
Many modern solutions integrate both capabilities into an Intrusion Detection and Prevention System (IDPS), offering a comprehensive defense mechanism that not only detects but also actively counters malicious activities, thereby fortifying the Wi-Fi network against sophisticated attackers.
Types of Intrusion Detection Systems
Various types of intrusion detection systems are deployed to secure different facets of a network, each with its own specialized focus. Network Intrusion Detection Systems (NIDS) monitor entire network segments for suspicious network traffic, often leveraging signature-based detection or anomaly detection. Host-based Intrusion Detection Systems (HIDS) focus on individual endpoints, analyzing system logs and file integrity to detect unauthorized changes or malicious processes.
Specifically for wireless environments, Wireless IDS (WIDS) solutions are designed to scrutinize 802.11 Wi-Fi network traffic, identifying various threats:
| Threat Type | Description |
| Rogue Access Points | Unauthorized access points that can compromise network security. |
| Man-in-the-Middle Attacks | Eavesdropping and potential alteration of communication between two parties. |
| Denial-of-Service (DoS) Attacks | Attempts to make a network resource unavailable to its intended users. |
Integrating these various IDS solutions provides a multi-layered approach to threat detection, ensuring comprehensive protection against a broad spectrum of potential threats.
Wi-Fi Security and Threats

Common Wi-Fi Security Vulnerabilities
Wireless networks, despite their pervasive convenience, are inherently susceptible to a range of security vulnerabilities that can compromise network security and data integrity. One of the most prevalent weaknesses lies in misconfigured access points (APs), which can inadvertently expose the Wi-Fi network to unauthorized access if default settings are not adequately secured or if strong authentication protocols are not enforced. Another significant vulnerability stems from the use of weak or outdated encryption standards, such as WEP, which can be easily circumvented by an attacker, leading to successful wireless intrusion. Furthermore, the absence of robust intrusion detection systems can leave an organization blind to potential threats, allowing malicious activities to proliferate unnoticed and undermining the overall security posture of the Wi-Fi network.
Denial of Service (DoS) Attacks on Wireless Networks
Denial of Service (DoS) attacks represent a formidable threat to network performance and operational continuity within wireless networks. These malicious activities are designed to overload an access point or an entire Wi-Fi network, thereby preventing legitimate users from accessing network resources. In a wireless context, a common DoS attack involves flooding the 802.11 network with de-authentication or disassociation frames, forcibly disconnecting clients from the access point. This not only disrupts service but can also be a precursor to more sophisticated attacks, such as a man-in-the-middle attack, where an attacker intercepts traffic as clients attempt to reconnect. A robust Wireless Intrusion Detection System (WIDS) is essential for real-time threat detection, capable of identifying the anomaly in network traffic and alerting administrators to such potential threats before they cripple the network.
Emerging Threats in Wireless Networking
The landscape of wireless networking is continually evolving, and with it, new and sophisticated threats emerge that demand advanced intrusion detection and prevention strategies. Beyond traditional DoS and man-in-the-middle attacks, organizations now face challenges from advanced persistent threats (APTs) specifically targeting Wi-Fi infrastructure, which aim for prolonged unauthorized access rather than immediate disruption. The proliferation of IoT devices on Wi-Fi networks also introduces new vulnerabilities, as many of these devices lack robust security features, becoming easy targets for an attacker to pivot into the main network. Effective network security now requires a proactive approach, leveraging advanced anomaly detection and sophisticated network traffic analysis, often integrating with open-source tools like Snort, to detect subtle indicators of malicious activities and ensure comprehensive protection against wireless intrusion.
Implementing a Wireless Intrusion Detection System
Steps for Deploying WIDS
Deploying a robust Wireless Intrusion Detection System (WIDS) involves several critical steps to ensure comprehensive network security and effective threat detection. Initially, a thorough site survey is paramount to identify optimal placement for wireless sensors, ensuring maximum coverage and visibility across the entire Wi-Fi network. Subsequently, the WIDS must be meticulously configured, which includes defining security policies, establishing baselines for normal network traffic, and integrating with existing network infrastructure and security information and event management (SIEM) systems. Continuous monitoring and regular calibration are then essential to fine-tune the system’s sensitivity, minimize false positives, and adapt to evolving wireless network conditions and emerging threats, thereby ensuring proactive intrusion detection.
Best Practices for Effective WIDS
For an effective Wireless Intrusion Detection System (WIDS) to truly fortify network security, adherence to best practices is indispensable. Regular updates of signature-based detection databases are crucial to combat new forms of malicious activities and zero-day vulnerabilities. Furthermore, consistently performing network traffic analysis helps in identifying unusual patterns or anomalies that might indicate a sophisticated wireless intrusion attempt. Organizations must also prioritize employee training on secure Wi-Fi practices and the importance of reporting suspicious activity. Integrating the WIDS with other intrusion detection and prevention systems (IDPS) and leveraging open-source tools like Snort for enhanced threat intelligence significantly bolsters overall threat detection capabilities, ensuring a resilient defense against potential threats and unauthorized access.
Evaluating WIDS Solutions
When evaluating various Wireless Intrusion Detection System (WIDS) solutions, organizations must meticulously assess several key factors to ensure the chosen system aligns with their specific network security requirements. Critical considerations include the solution’s ability for real-time anomaly detection and signature-based detection, its scalability to accommodate future network expansion, and its seamless integration capabilities with existing IT infrastructure and security tools. Assessing the effectiveness of its network traffic analysis engine, its capacity to detect various types of malicious activities such as man-in-the-middle and Denial of Service (DoS) attacks, and the clarity of its alert mechanisms are also vital. A comprehensive evaluation ensures that the chosen WIDS solution provides robust protection against wireless intrusion and potential threats, delivering true value for money and peace of mind.
Future of Wireless Network Intrusion Detection
Trends in WIDS Technology
The future of Wireless Intrusion Detection System (WIDS) technology is characterized by several transformative trends aimed at enhancing threat detection capabilities and adapting to the dynamic landscape of wireless networks. We anticipate a greater emphasis on integrating machine learning and artificial intelligence into WIDS solutions, moving beyond traditional signature-based detection towards more sophisticated anomaly detection that can identify subtle indicators of wireless intrusion. The proliferation of 5G and Wi-Fi 6 will necessitate WIDS capable of analyzing higher bandwidths and more complex 802.11 protocols, demanding real-time traffic analysis at unprecedented speeds. Furthermore, the convergence of WIDS with endpoint security and cloud-based security platforms will offer a more holistic and unified approach to network security, ensuring comprehensive protection against evolving potential threats.
Integrating AI with Intrusion Detection Systems
The integration of Artificial Intelligence (AI) with Intrusion Detection Systems (IDS) marks a pivotal advancement in combating sophisticated malicious activities and ensuring robust network security. AI-driven IDS solutions, such as those offered by TeamWin Global Technologica’s enterprise AI-driven next-generation firewalls, leverage advanced algorithms to analyze network traffic with unparalleled precision, moving beyond conventional signature-based detection. This allows for superior anomaly detection, enabling the system to learn normal network behavior and swiftly identify deviations indicative of a wireless intrusion or a zero-day vulnerability, often in real time. This proactive approach significantly enhances threat detection, empowering organizations to anticipate and mitigate cyber risks through vigilant monitoring and swift response strategies, thereby fortifying the Wi-Fi network against even the most elusive attackers.
The Role of WIDS in Future Cybersecurity Strategies
The role of a Wireless Intrusion Detection System (WIDS) in future cybersecurity strategies is set to expand significantly, becoming an even more indispensable component of a layered defense architecture. As wireless networks continue to be the primary conduit for data, WIDS will evolve beyond mere intrusion detection to become integral to broader threat intelligence platforms. It will play a crucial role in correlating wireless intrusion events with other security data, providing a more comprehensive view of an organization’s security posture. This integration will enable predictive analytics and automated response capabilities, allowing for proactive mitigation of potential threats and vulnerabilities across the entire Wi-Fi network. The continued evolution of WIDS will ensure robust network security, safeguarding enterprises against the constantly evolving landscape of cyber risks and ensuring tomorrow’s success.
How do intrusion detection and prevention systems detect attacks over Wi‑Fi and visualize network activity?
Intrusion detection and prevention systems monitor wireless traffic for anomalous signatures and behaviors to detect attacks, combining packet inspection, MAC address tracking, SSID analysis and signal strength mapping to build a visualization of network activity. Many systems provide a dashboard that correlates events, highlights network vulnerabilities and displays network IDs and clients that may be compromised. Visualization and automation features help security teams detect and respond to security threats faster by surfacing malicious patterns such as brute force attempts, rogue APs, or malware beaconing.
Can intrusion detection and prevention systems prevent denial of service attack and other cyberattack types on a vulnerable router or SSID?
Yes, intrusion detection and prevention systems can mitigate denial of service attack vectors and other cyberattacks against a router or SSID by applying real‑time policies: dropping malicious frames, rate limiting, quarantining devices by MAC address and blocking suspicious SSIDs. While they reduce exposure to network vulnerable points and known network vulnerabilities, they are part of layered security measures and should be combined with proper encryption, secure router configuration and vendor security products from firms like Cisco for stronger protection.
How do IDS/IPS handle false alarms and anomalous behavior to accurately detect attacks over Wi‑Fi?
Modern intrusion detection and prevention systems use anomaly analyzers, signature feeds and machine learning to distinguish true security threats from benign anomalies. Tuning reduces false alarms by baselining normal network activity and leveraging automation to correlate events across access points, signal strength variations and device MAC address changes. Administrators can refine thresholds on the dashboard and use contextual data—such as network IDs, behavioral baselines and known malware indicators—to improve detect attacks accuracy.
What role do tools like aircrack‑ng and a wireless analyzer play alongside intrusion detection and prevention systems?
Tools such as aircrack‑ng and wireless analyzers complement intrusion detection and prevention systems by providing packet‑level analysis and penetration testing to discover network vulnerabilities, test encryption strength, and simulate attacks. Security teams use these tools to validate IDS/IPS rules, expose weak SSIDs or misconfigured routers, and assess how security products respond to crafted frames or targeted malware activity. Results feed back into IDS/IPS configurations to improve detect and respond workflows.
How should organizations integrate intrusion detection and prevention systems into their security measures and incident response?
Organizations should integrate intrusion detection and prevention systems into a broader security program that includes encryption, endpoint protection, regular vulnerability scans and incident response playbooks. Connect IDS/IPS alerts to a centralized dashboard or SIEM for correlation, enable automated containment actions for high‑confidence detections, and establish procedures to investigate MAC address anomalies, prioritize alerts to reduce false alarms, and escalate suspected cyberattack events. Combining vendor solutions like Cisco network ids with in‑house analyzers and visualization tools improves the ability to detect attacks and rapidly detect and respond to threats.