BIND DNS Servers Hit by 14 Security Flaws Enabling Cache Poisoning and Remote Crashes
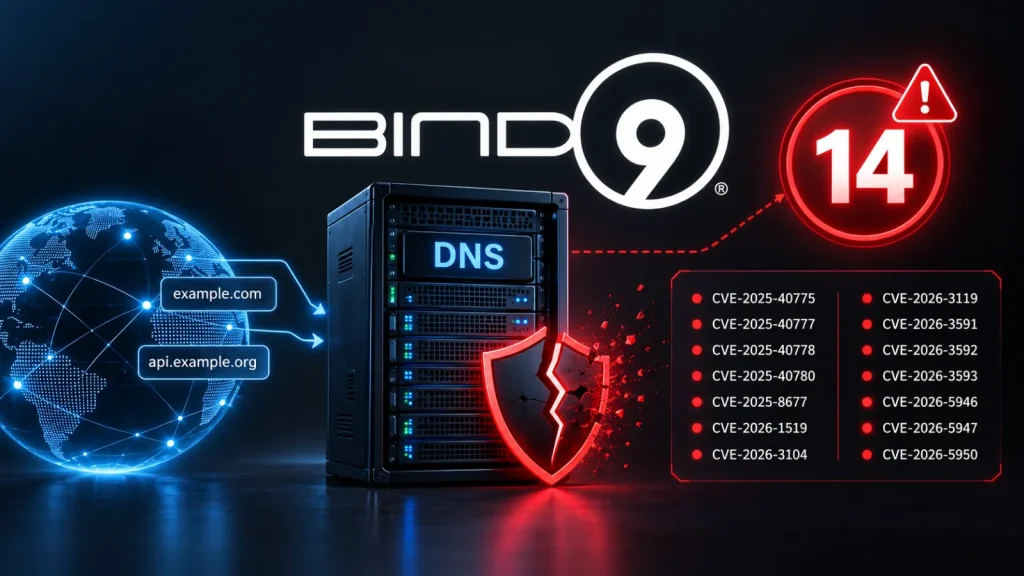
DNS, the Internet’s phonebook, underpins nearly every online interaction. When a fundamental component like BIND (Berkeley Internet Name Domain) encounters significant security vulnerabilities, the implications can ripple across the entire digital landscape. Recently, the Internet Systems Consortium (ISC) issued critical security updates for BIND 9, addressing a concerning cluster of 14 flaws. These vulnerabilities pose serious risks, from cache poisoning to remote server crashes, making immediate patching a paramount concern for administrators worldwide.
Understanding the BIND Vulnerabilities
The ISC’s recent disclosure highlights a series of security flaws impacting BIND 9, a widely deployed DNS server software. These 14 vulnerabilities, discovered and subsequently patched, present a multifaceted threat to the integrity and availability of DNS services. While the specific technical details of each flaw vary, their collective potential for disruption is substantial.
Key Threat Vectors
- Cache Poisoning: Attackers could inject forged DNS records into a BIND server’s cache. This allows them to redirect users to malicious websites, facilitating phishing attacks, malware distribution, or man-in-the-middle operations.
- Remote Server Crashes: Several vulnerabilities could be exploited to remotely trigger a denial-of-service (DoS) condition, causing BIND servers to crash or become unresponsive. This directly impacts an organization’s ability to resolve domain names, effectively taking their services offline.
- Resource Exhaustion: Attackers might craft specific queries or traffic patterns designed to consume excessive server resources, leading to performance degradation or service disruption without a full crash.
- DNSSEC Bypass: For organizations relying on DNS Security Extensions (DNSSEC) for enhanced authentication and data integrity, certain flaws could potentially bypass these protections, undermining the trustworthiness of DNS resolutions.
The most severe of these issues primarily affect the named daemon, the core component responsible for handling DNS queries and responses. Administrators running recursive BIND resolvers, which are common in many network infrastructures, are particularly urged to prioritize these updates.
Specific CVEs and Their Impact
The ISC has assigned several Common Vulnerabilities and Exposures (CVEs) to these newly discovered flaws. Understanding these identifiers is crucial for tracking and remediation.
- CVE-2023-3341: This vulnerability concerns a potential cache poisoning issue, allowing an attacker to insert arbitrary records into the cache.
- CVE-2023-3342: A flaw that could lead to remote denial of service by triggering an assertion failure in specific scenarios.
- CVE-2023-3343: Another denial-of-service vulnerability, this one related to processing certain malformed responses.
- CVE-2023-3344: This CVE points to a resource exhaustion issue through specially crafted queries.
- CVE-2023-3345: A DNSSEC bypass concern, potentially allowing forged responses to be accepted despite DNSSEC validation.
- CVE-2023-3346: This flaw could lead to a server crash under specific query conditions.
- CVE-2023-3347: Another denial-of-service risk, impacting servers processing certain types of queries.
- CVE-2023-3348: Potential for a server crash when handling specific malformed records.
- CVE-2023-3349: This vulnerability addresses a logic error that could lead to incorrect DNSSEC validation.
- CVE-2023-3350: Another resource exhaustion vulnerability.
- CVE-2023-3351: A flaw that could cause a recursive resolver to crash when processing specific responses.
- CVE-2023-3352: This vulnerability relates to an issue in handling certain NS records, leading to a crash.
- CVE-2023-3353: A denial-of-service vulnerability due to improper handling of specific data types.
- CVE-2023-3354: This final CVE highlights a potential issue with zone transfers, possibly leading to a crash.
Remediation Actions
Given the severity and widespread impact of these vulnerabilities, immediate action is critical for any organization operating BIND DNS servers.
- Update BIND 9: The most crucial step is to apply the latest patched releases provided by the Internet Systems Consortium. Ensure your BIND installation is updated to a version that addresses these CVEs. Consult the official ISC website for specific version numbers and upgrade paths.
- Monitor DNS Traffic: Implement robust DNS traffic monitoring to detect anomalies that might indicate attempted exploitation. Look for unusually high query volumes, malformed queries, or suspicious responses.
- Review Configuration: Periodically audit your BIND configuration for best practices and unnecessary open ports or services. Ensure that only essential functionalities are exposed.
- Implement Rate Limiting: Configure rate limiting for recursive queries to mitigate the impact of denial-of-service attacks that exploit resource exhaustion vulnerabilities.
- DNSSEC Validation: While some flaws target DNSSEC, maintaining proper DNSSEC validation on your recursive resolvers remains vital. Ensure your configurations are correct and up-to-date.
- Firewall Rules: Restrict inbound access to your BIND servers to only necessary IP addresses and ports. Implement strong firewall rules at the network perimeter.
Tools for DNS Security and Monitoring
To aid in detecting, mitigating, and generally strengthening DNS security, several tools are invaluable:
| Tool Name | Purpose | Link |
|---|---|---|
| ISC BIND Software | Official software and patched releases for BIND 9. | https://www.isc.org/bind/ |
| Wireshark | Network protocol analyzer for deep inspection of DNS traffic. | https://www.wireshark.org/ |
| dnscat2 | Tool for C2 over DNS, useful for understanding DNS-based attacks. | https://github.com/iagox86/dnscat2 |
| DNSLint | Microsoft utility for diagnosing common DNS name resolution issues. | https://support.microsoft.com/en-us/topic/description-of-the-dnslint-utility-0104e76d-1b15-1811-9257-27e1f40d2551 |
| Nagios Core / Zabbix | Network monitoring solutions to track DNS server health and performance. | https://www.nagios.org/ https://www.zabbix.com/ |
| RPZ (Response Policy Zones) | BIND feature for blacklisting malicious domains or IP addresses. | https://www.isc.org/docs/rpz.pdf |
Conclusion
The discovery of 14 security flaws in BIND DNS servers underscores the continuous need for vigilance in network infrastructure management. These vulnerabilities, ranging from cache poisoning to remote crashes, have the potential for significant disruption and compromise. System administrators operating BIND 9 are strongly advised to apply the latest security updates provided by the ISC without delay. Proactive patching, coupled with robust monitoring and adherence to DNS security best practices, remains the most effective defense against these evolving threats.