FamousSparrow Exploits Public-Facing Exchange Servers to Deploy SparroWocky Backdoor
Unmasking SparroWocky: FamousSparrow’s Latest Threat to Microsoft Exchange Servers
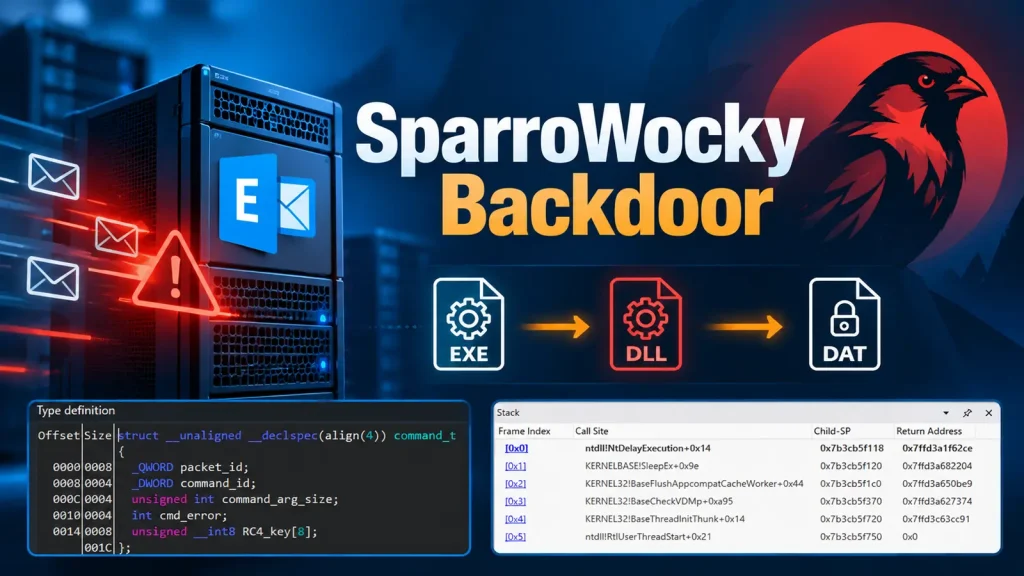
The digital landscape is constantly under siege, and nowhere is this more evident than in the persistent targeting of critical infrastructure. Recently, the notorious espionage group FamousSparrow has unveiled a new, potent backdoor dubbed SparroWocky, leveraging exploited public-facing Microsoft Exchange servers. This development underscores a significant threat, transforming what should be a robust communication hub into a covert, long-term entry point within government networks and beyond.
The implications of this campaign extend far beyond the initial breach. Email servers, by their very nature, are repositories of sensitive communications and often serve as trusted conduits within an organization. A compromise of this magnitude offers an adversary unparalleled access and persistence.
FamousSparrow: A Persistent Espionage Threat
FamousSparrow is not a new player in the realm of advanced persistent threats (APTs). Known for its sophisticated tactics and strategic targeting, this group consistently seeks to compromise high-value targets, particularly within government and critical sectors. Their shift to deploying SparroWocky through public-facing Exchange servers highlights an adaptation to commonly exposed attack surfaces, maximizing their potential for widespread impact and stealthy infiltration.
SparroWocky: A Deep Dive into the New Backdoor
While specific technical details regarding SparroWocky are still emerging, its deployment through compromised Microsoft Exchange servers immediately raises red flags. Backdoors of this nature are designed for persistent access, often employing stealthy communication channels and evasion techniques to remain undetected for extended periods. This allows attackers to:
- Maintain a foothold within the compromised network.
- Exfiltrate sensitive data, including emails, documents, and intellectual property.
- Move laterally within the network to access other critical systems.
- Establish command and control (C2) infrastructure for long-term operations.
The choice of Exchange servers as the primary entry vector is strategic. These servers handle an immense volume of an organization’s most critical data, making them an invaluable target for espionage groups like FamousSparrow.
The Criticality of Public-Facing Exchange Server Security
The FamousSparrow campaign serves as a stark reminder of the paramount importance of securing all public-facing assets, especially those as integral as Microsoft Exchange servers. These systems, when exposed and unpatched, become prime targets for exploitation. This is not merely about preventing a single incident; it’s about safeguarding the very fabric of an organization’s communication and data integrity.
Past vulnerabilities, such as those related to CVE-2021-26855 (ProxyLogon) and subsequent related exploits, have demonstrated the devastating consequences of unpatched Exchange servers. While the specific CVEs exploited by FamousSparrow for SparroWocky’s initial deployment are not explicitly detailed in the source, the pattern suggests the group is likely leveraging known, or potentially zero-day, vulnerabilities to gain initial access.
Remediation Actions and Proactive Defense Strategies
Defending against threats like SparroWocky requires a multi-layered and proactive approach. Organizations must prioritize the security of their Microsoft Exchange infrastructure to mitigate the risk of falling victim to such sophisticated attacks.
- Patch Management: Implement a rigorous and timely patch management program for all Microsoft Exchange servers. This includes applying security updates, cumulative updates, and any other relevant hotfixes as soon as they are released.
- Network Segmentation: Isolate Exchange servers from other critical network segments to limit lateral movement in the event of a breach.
- Strong Authentication: Enforce multi-factor authentication (MFA) for all administrative access to Exchange servers and for all user accounts, where feasible.
- Monitoring and Logging: Implement comprehensive logging on Exchange servers and integrate these logs with a Security Information and Event Management (SIEM) system for real-time monitoring and anomaly detection. Look for unusual login attempts, unauthorized access to mailboxes, and suspicious process execution.
- Endpoint Detection and Response (EDR): Deploy EDR solutions on all Exchange servers to detect and respond to malicious activities, including the presence of backdoors like SparroWocky.
- Regular Audits and Penetration Testing: Conduct regular security audits and penetration tests specifically targeting your Exchange environment to identify and remediate vulnerabilities before attackers can exploit them.
- Incident Response Plan: Develop and regularly test a robust incident response plan specifically for email server compromises.
- Disable Unnecessary Services: Minimize the attack surface by disabling any unnecessary services or features on Exchange servers.
- Firewall Rules: Implement strict firewall rules to limit inbound and outbound traffic to only what is absolutely necessary for Exchange functionality.
Tools for Enhanced Exchange Server Security
Leveraging appropriate tools can significantly bolster your defense against threats targeting Microsoft Exchange servers.
| Tool Name | Purpose | Link |
|---|---|---|
| Microsoft Exchange Health Checker Script | Identifies common configuration issues and missing updates. | https://docs.microsoft.com/en-us/exchange/architecture/health-checker |
| Nessus | Vulnerability scanning for identifying known weaknesses in Exchange and other systems. | https://www.tenable.com/products/nessus |
| Microsoft Defender for Endpoint | EDR capabilities for threat detection and response on Exchange servers. | https://www.microsoft.com/en-us/security/business/endpoint-security/microsoft-defender-endpoint |
| Splunk (or other SIEM) | Centralized logging, correlation, and alerting for security events. | https://www.splunk.com/ |
Key Takeaways and Forward-Looking Security
The FamousSparrow campaign, deploying the SparroWocky backdoor via exploited Microsoft Exchange servers, serves as a critical warning. It highlights the persistent and evolving nature of nation-state threats and their focus on high-value targets. Organizations, particularly those within government and critical infrastructure, must recognize the immense risk posed by exposed email systems. A proactive, defense-in-depth strategy, centered around rigorous patching, robust monitoring, and comprehensive incident response, is not merely recommended but essential for safeguarding against these sophisticated and potentially devastating attacks.